Compliance Mapping
Which SOC 2, HIPAA, PCI-DSS and GDPR controls DBTrail can support as evidence, and what stays your responsibility.
DBTrail is not a certified product
These frameworks audit your organization, not tools. DBTrail is one technical control inside your program; it holds no certification of its own.
Backup and recovery
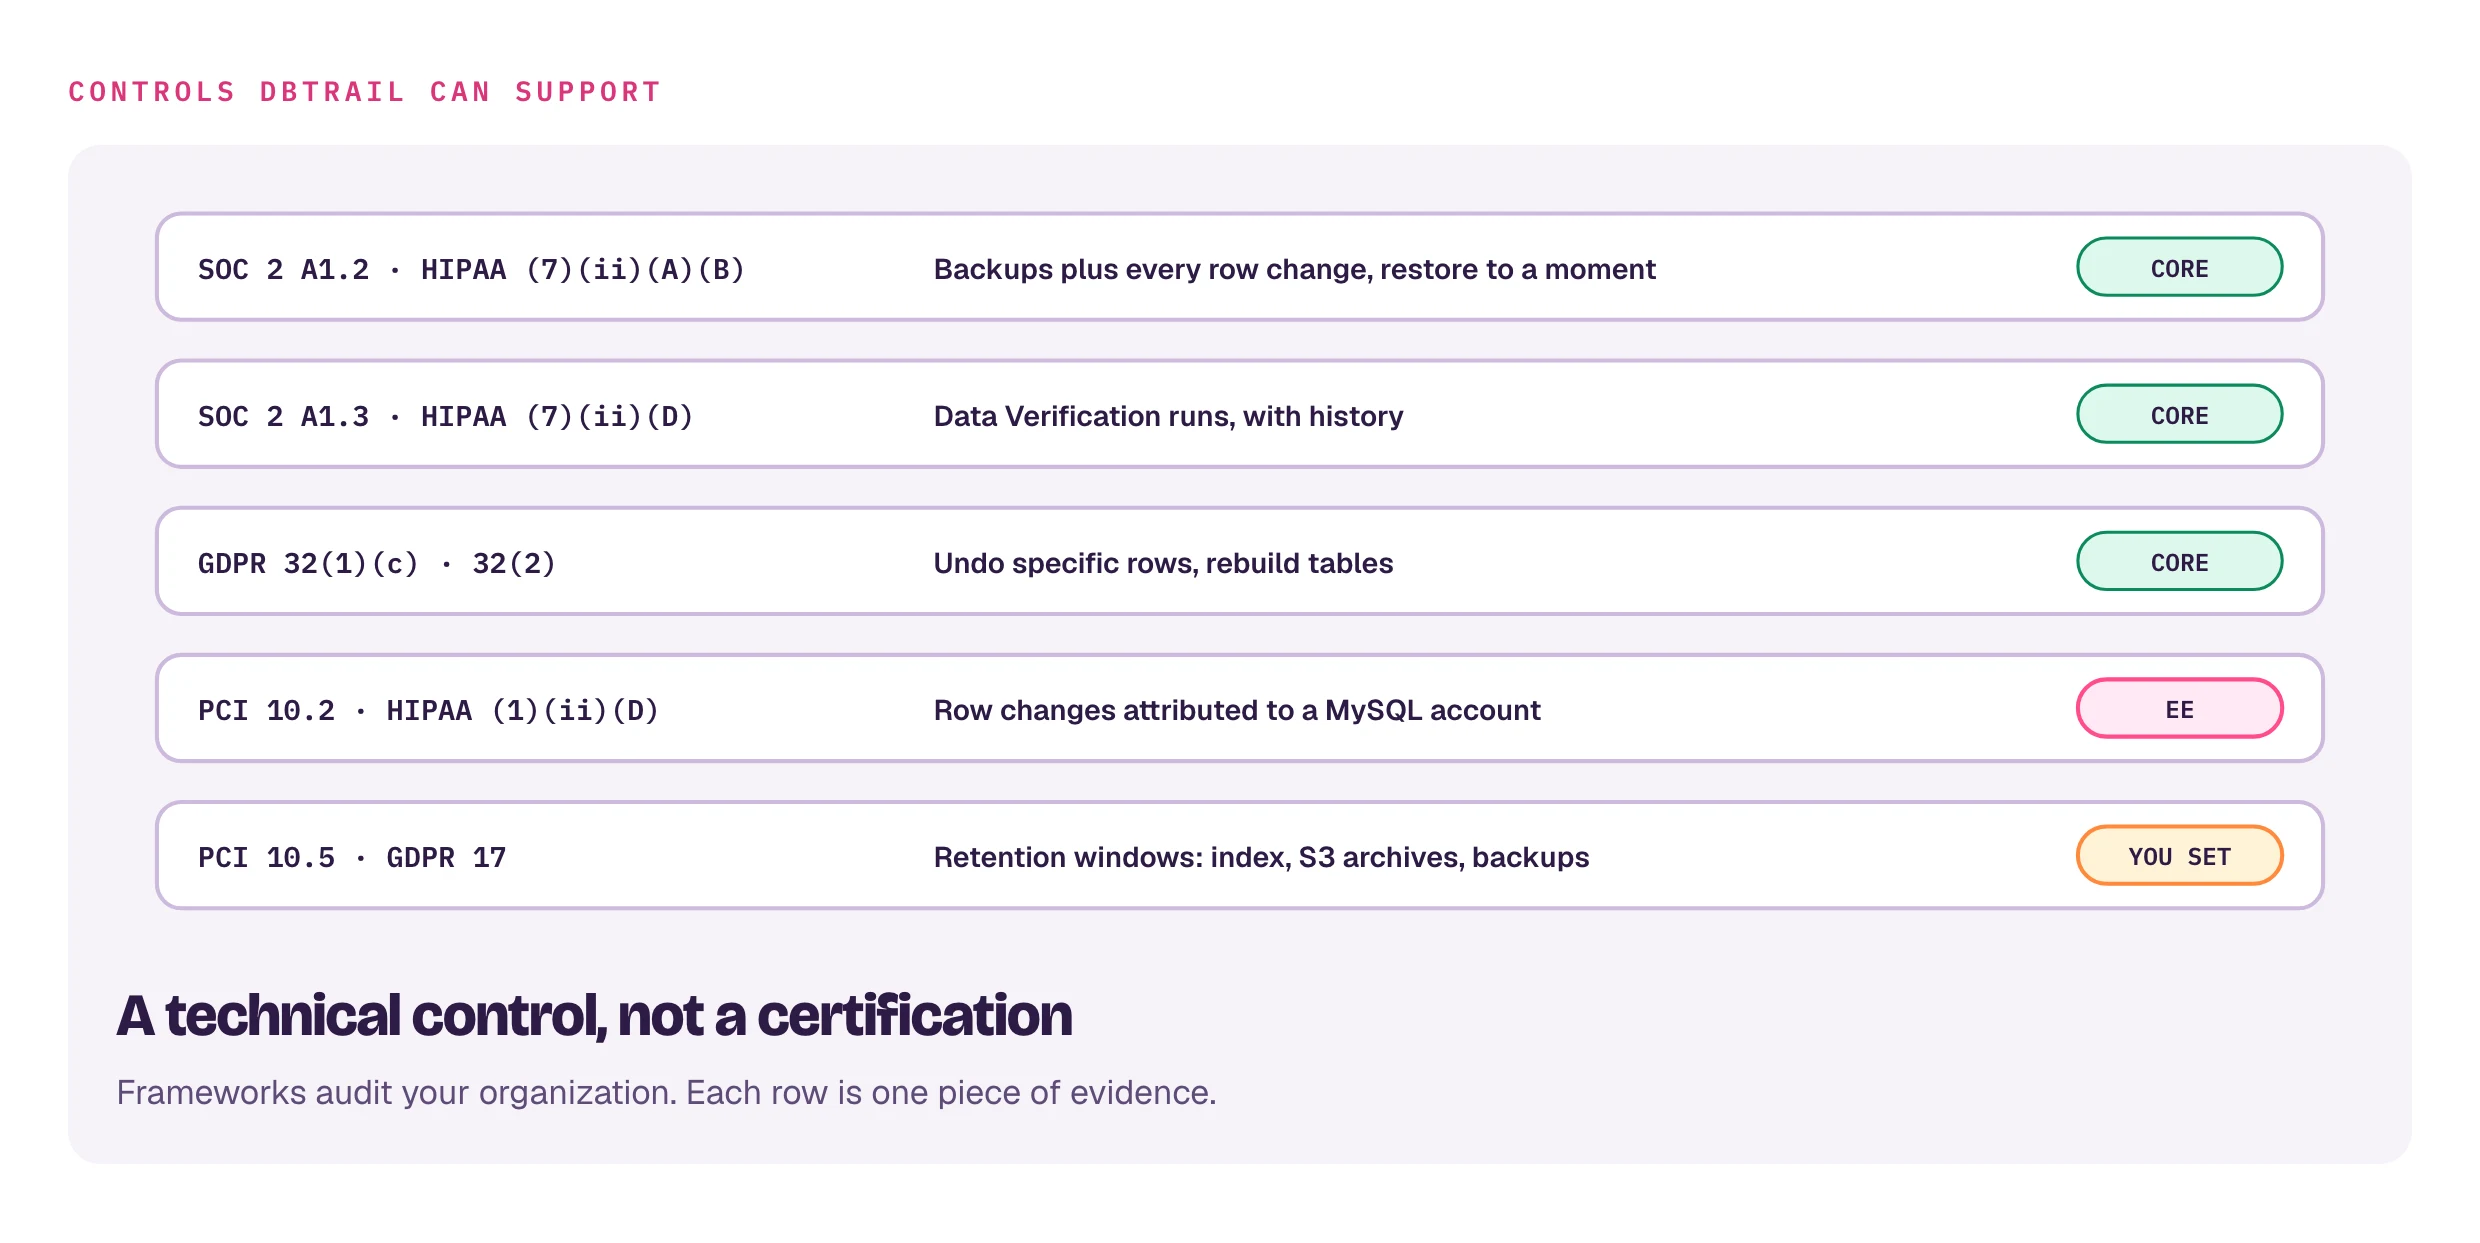
SOC 2 A1.2 · HIPAA §164.308(a)(7)(ii)(A) Data Backup Plan (required) · (ii)(B) Disaster Recovery Plan (required) · GDPR 32(1)(c)
- Every row change is captured from the binlog as it commits, with before and after images. How capture works.
- Logical backups on a per-server schedule from the Snapshots page. Snapshot strategy.
- Restore specific rows (Recovery) or whole tables at any second (Restore tables to a moment).
Testing recovery
SOC 2 A1.3 · HIPAA §164.308(a)(7)(ii)(D) Testing (addressable) · GDPR 32(1)(d)
Data Verification rebuilds tables from backups plus changes and compares them, table by table. Runs can be scheduled; Past checks keeps the last 20 runs per server. Verification settings.
Who changed data
PCI-DSS v4.0 10.2 · HIPAA §164.308(a)(1)(ii)(D) · GDPR 32(2)
- Capture records data-level changes, including direct SQL by privileged users or scripts that application logs miss.
- Each event carries the raw
connection_id.
Protecting the record
PCI-DSS 10.3
- DBTrail has no path that edits an indexed event. Rows leave the index by rotation, and after a crash the rows written past the last checkpoint are removed and read again.
- DBTrail never deletes archived objects from S3. For tamper resistance,
enable S3 Object Lock on the archive bucket;
bintrail doctor --archive-s3checks the bucket's posture. Object Lock guide.
Retention and erasure
PCI-DSS 10.5 · GDPR Article 17
| Where personal data lives | Retention |
|---|---|
| Live index | Settings → Rotation (default 30d; CLI --rotate-retain, off keeps everything) |
| S3 archives | Your bucket's lifecycle rules; archived hours stay queryable |
| Backups | Backup retention (Backup settings) and bucket lifecycle |
A 12-month PCI window needs archives kept 12 months. DBTrail has no per-row erasure: erasure requests are met by retention windows, so agree them with your DPO against minimums set by other frameworks. Retention settings.
Not covered
Offsite or cross-region replication, full infrastructure recovery, operating the index database (support scope), application-layer logging, SIEM, BAAs, DPIAs, encryption policy, access control programs and lawful basis documentation.
Audit support
For an audit that lists DBTrail as a control, we can provide architecture and
data flow documentation, retention configuration, verification output, and
the encryption options in use: TLS for the web interface, InnoDB tablespace
encryption for the index (bintrail init --encrypt, keyring plugin required)
and AES-256 encrypted dump files (bintrail dump --encrypt). Contact
hello@dbtrail.com.